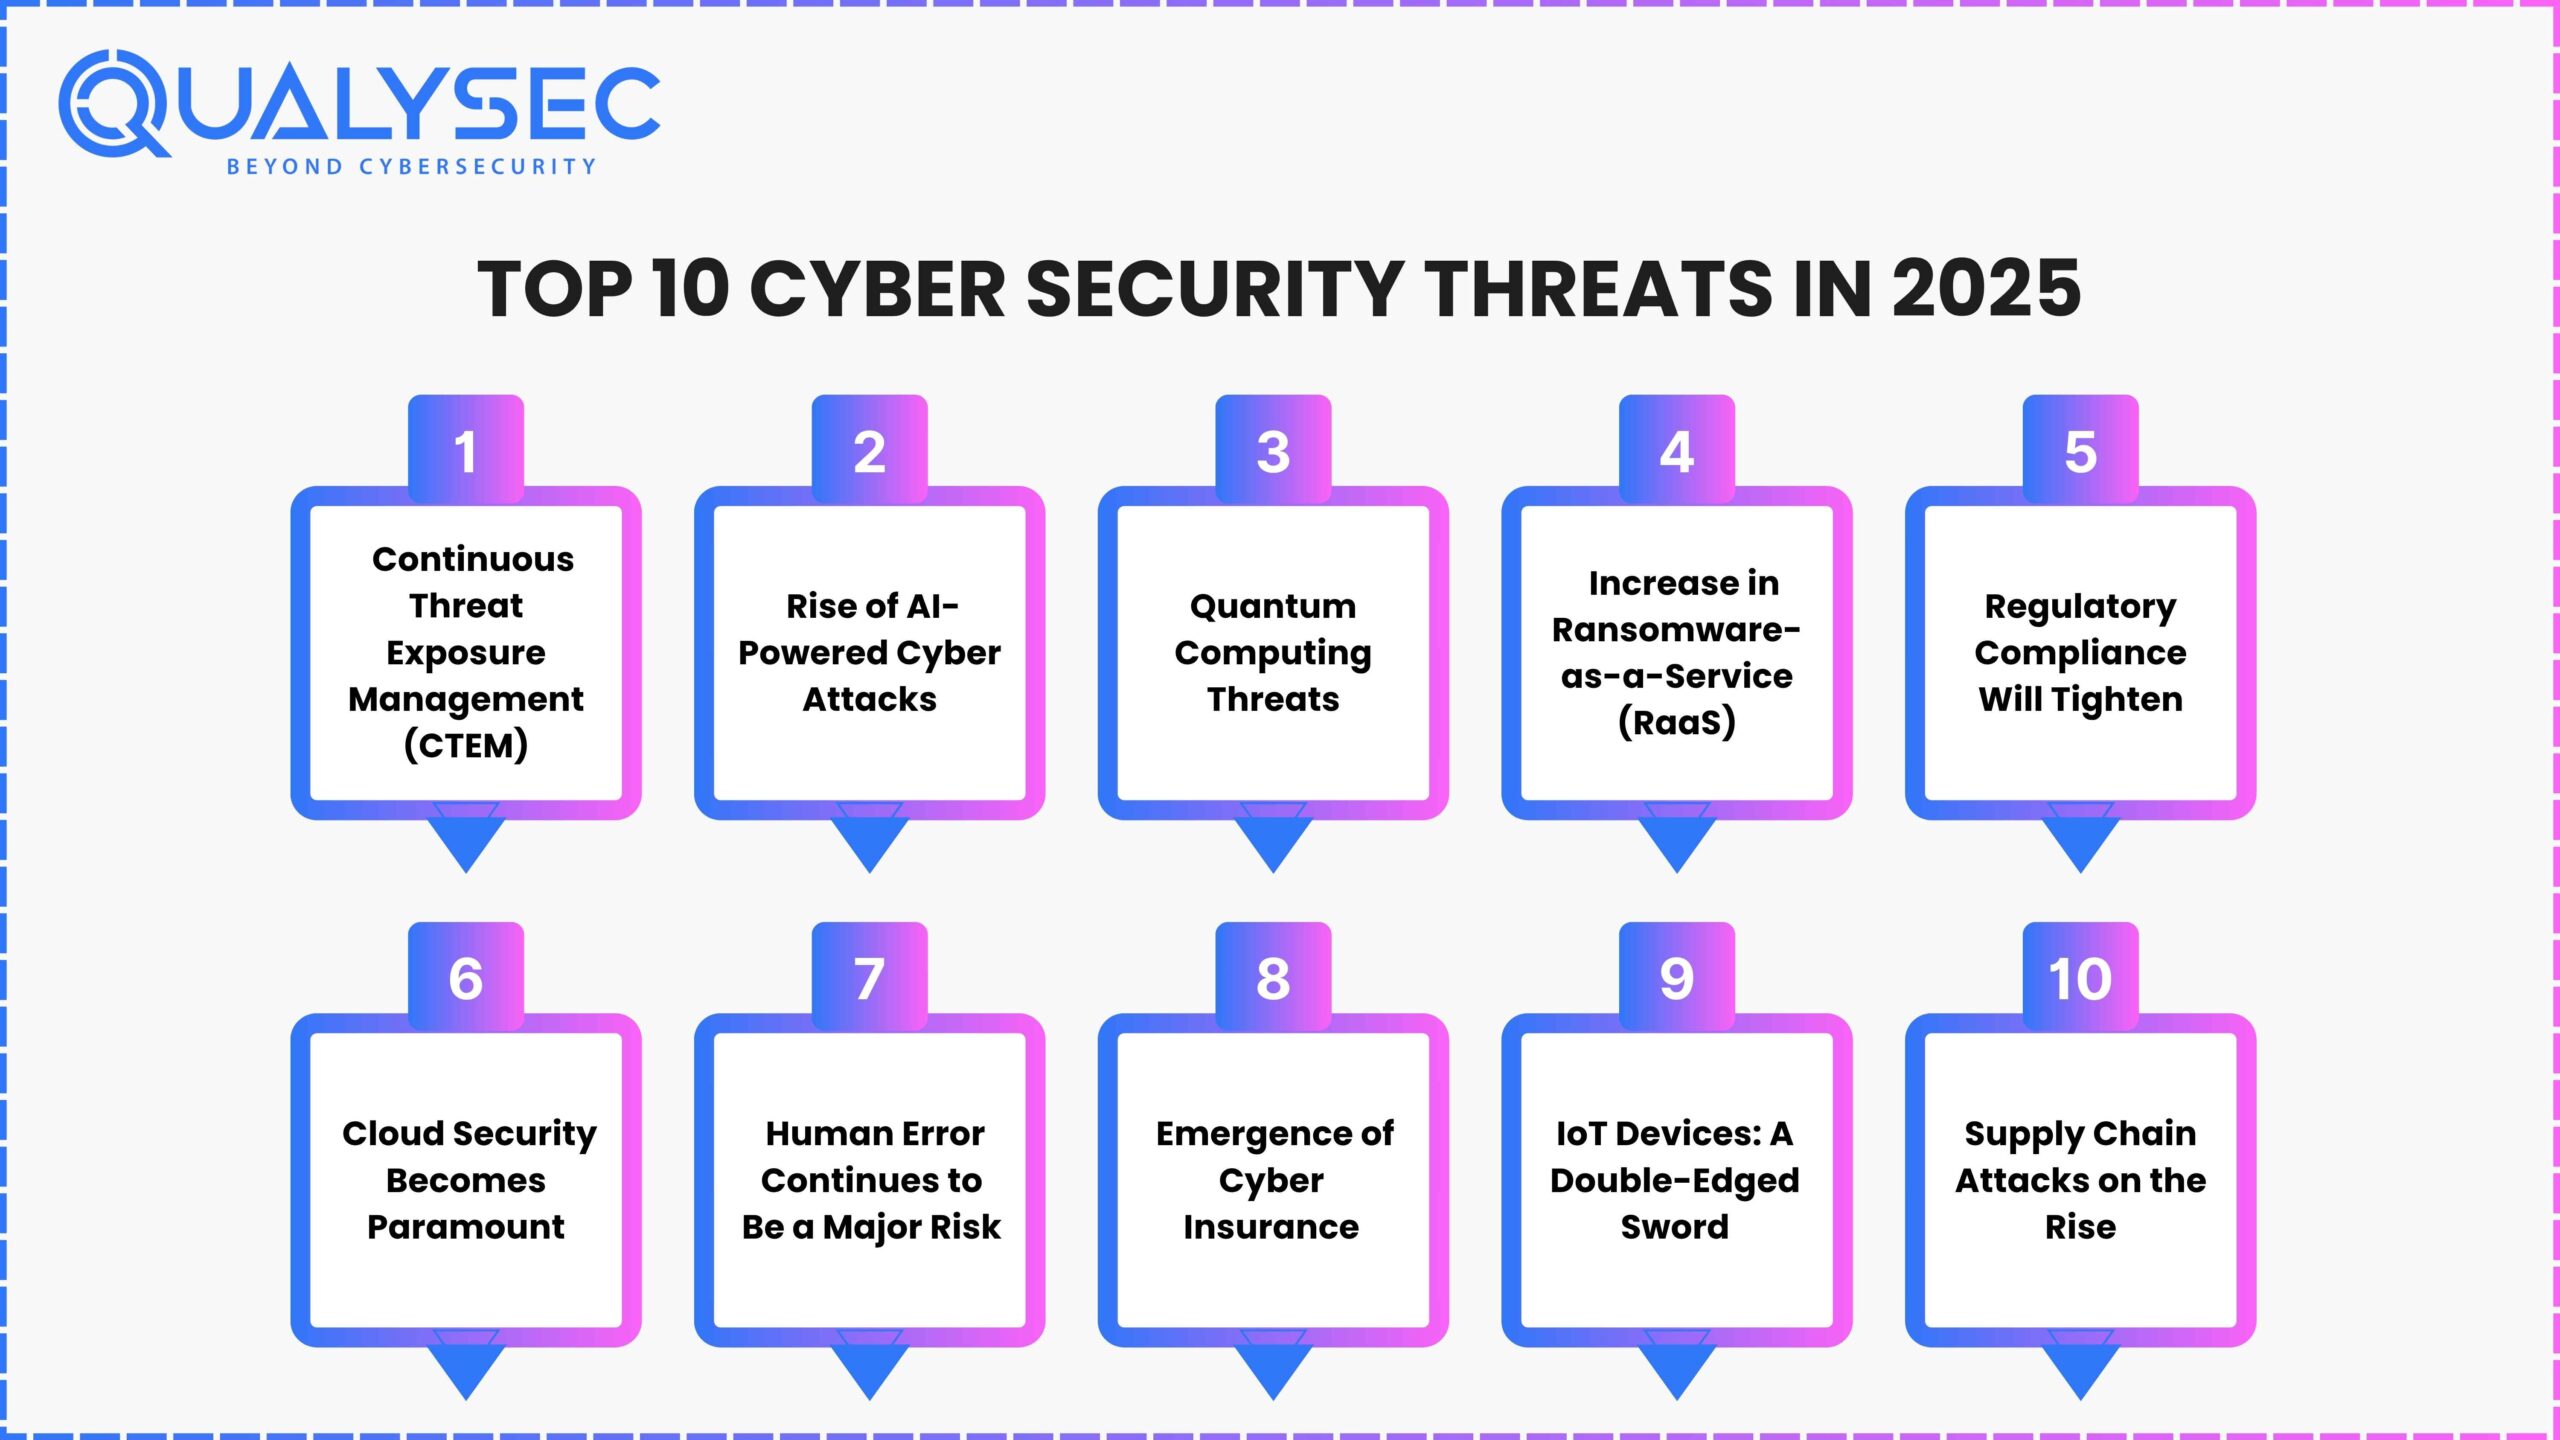
Modern cybersecurity operations require a standardized methodology to evaluate, communicate, and react to active digital risks. The cyber threat level serves as the foundational metric organizations and government agencies use to synchronize defensive postures against escalating digital attacks. Navigating this landscape requires understanding how threat levels are calculated, operationalized, and scaled across enterprise architectures.
Evolution of National and Enterprise Threat Frameworks
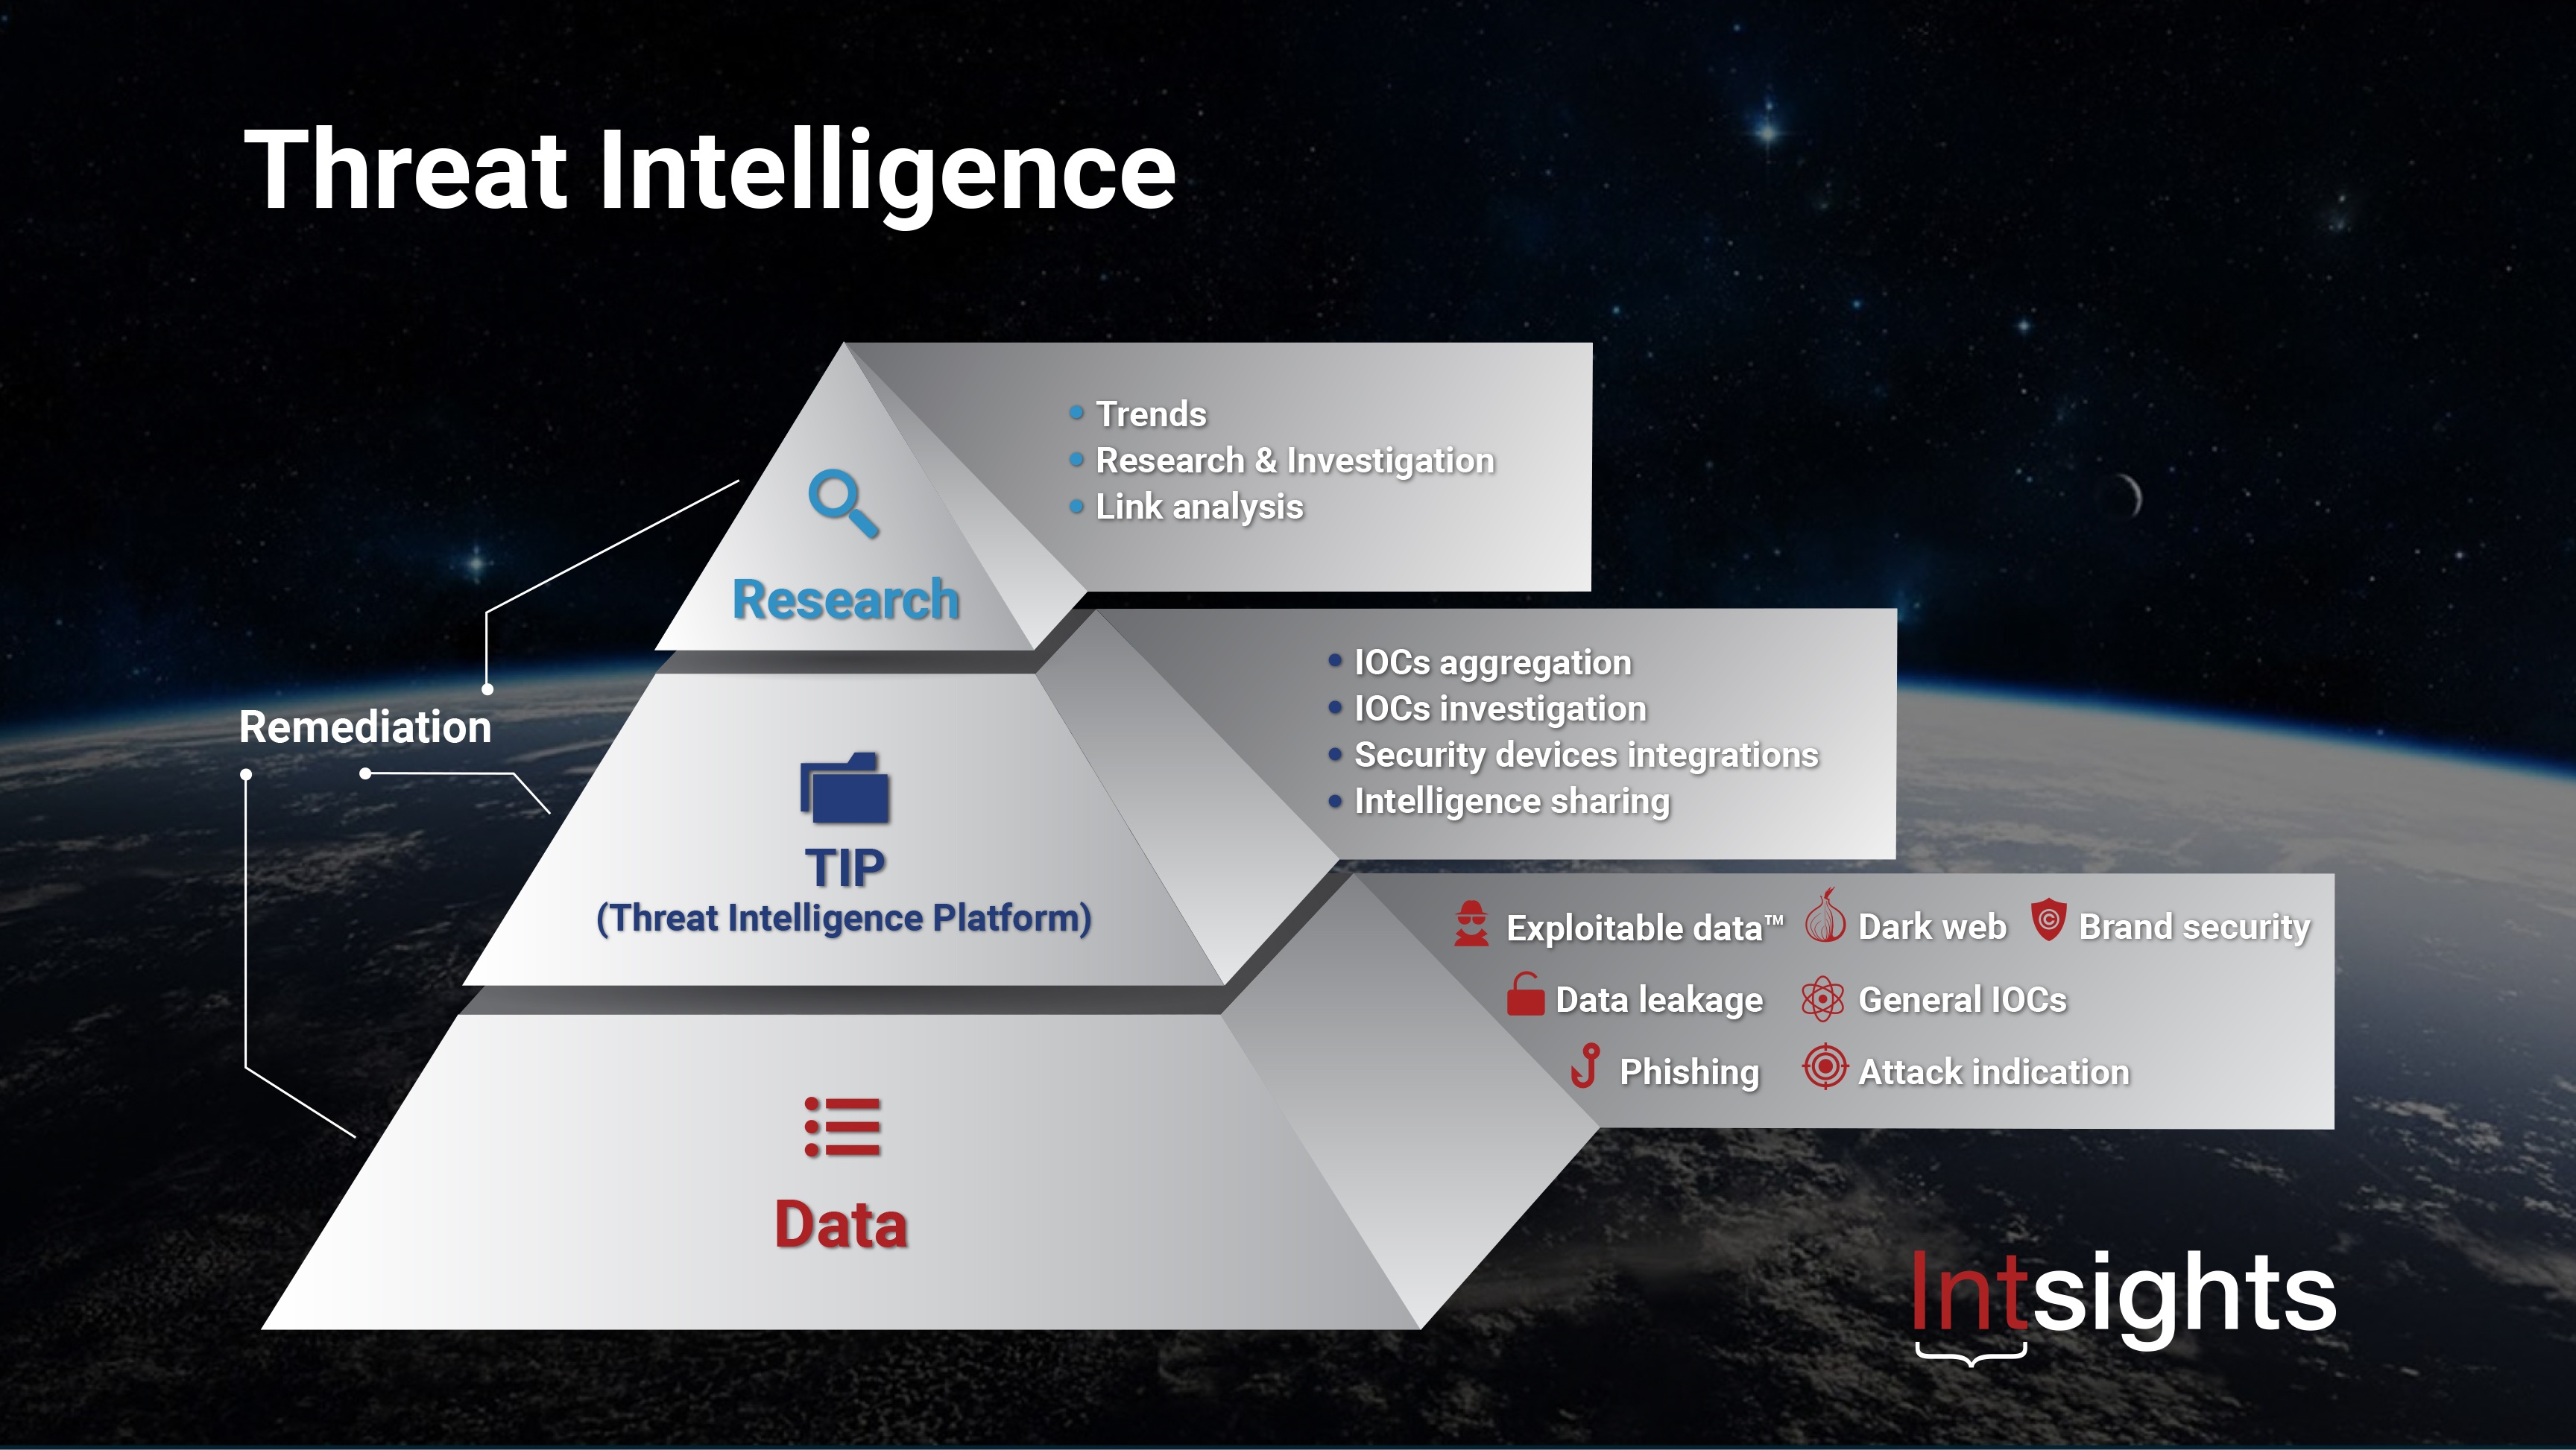
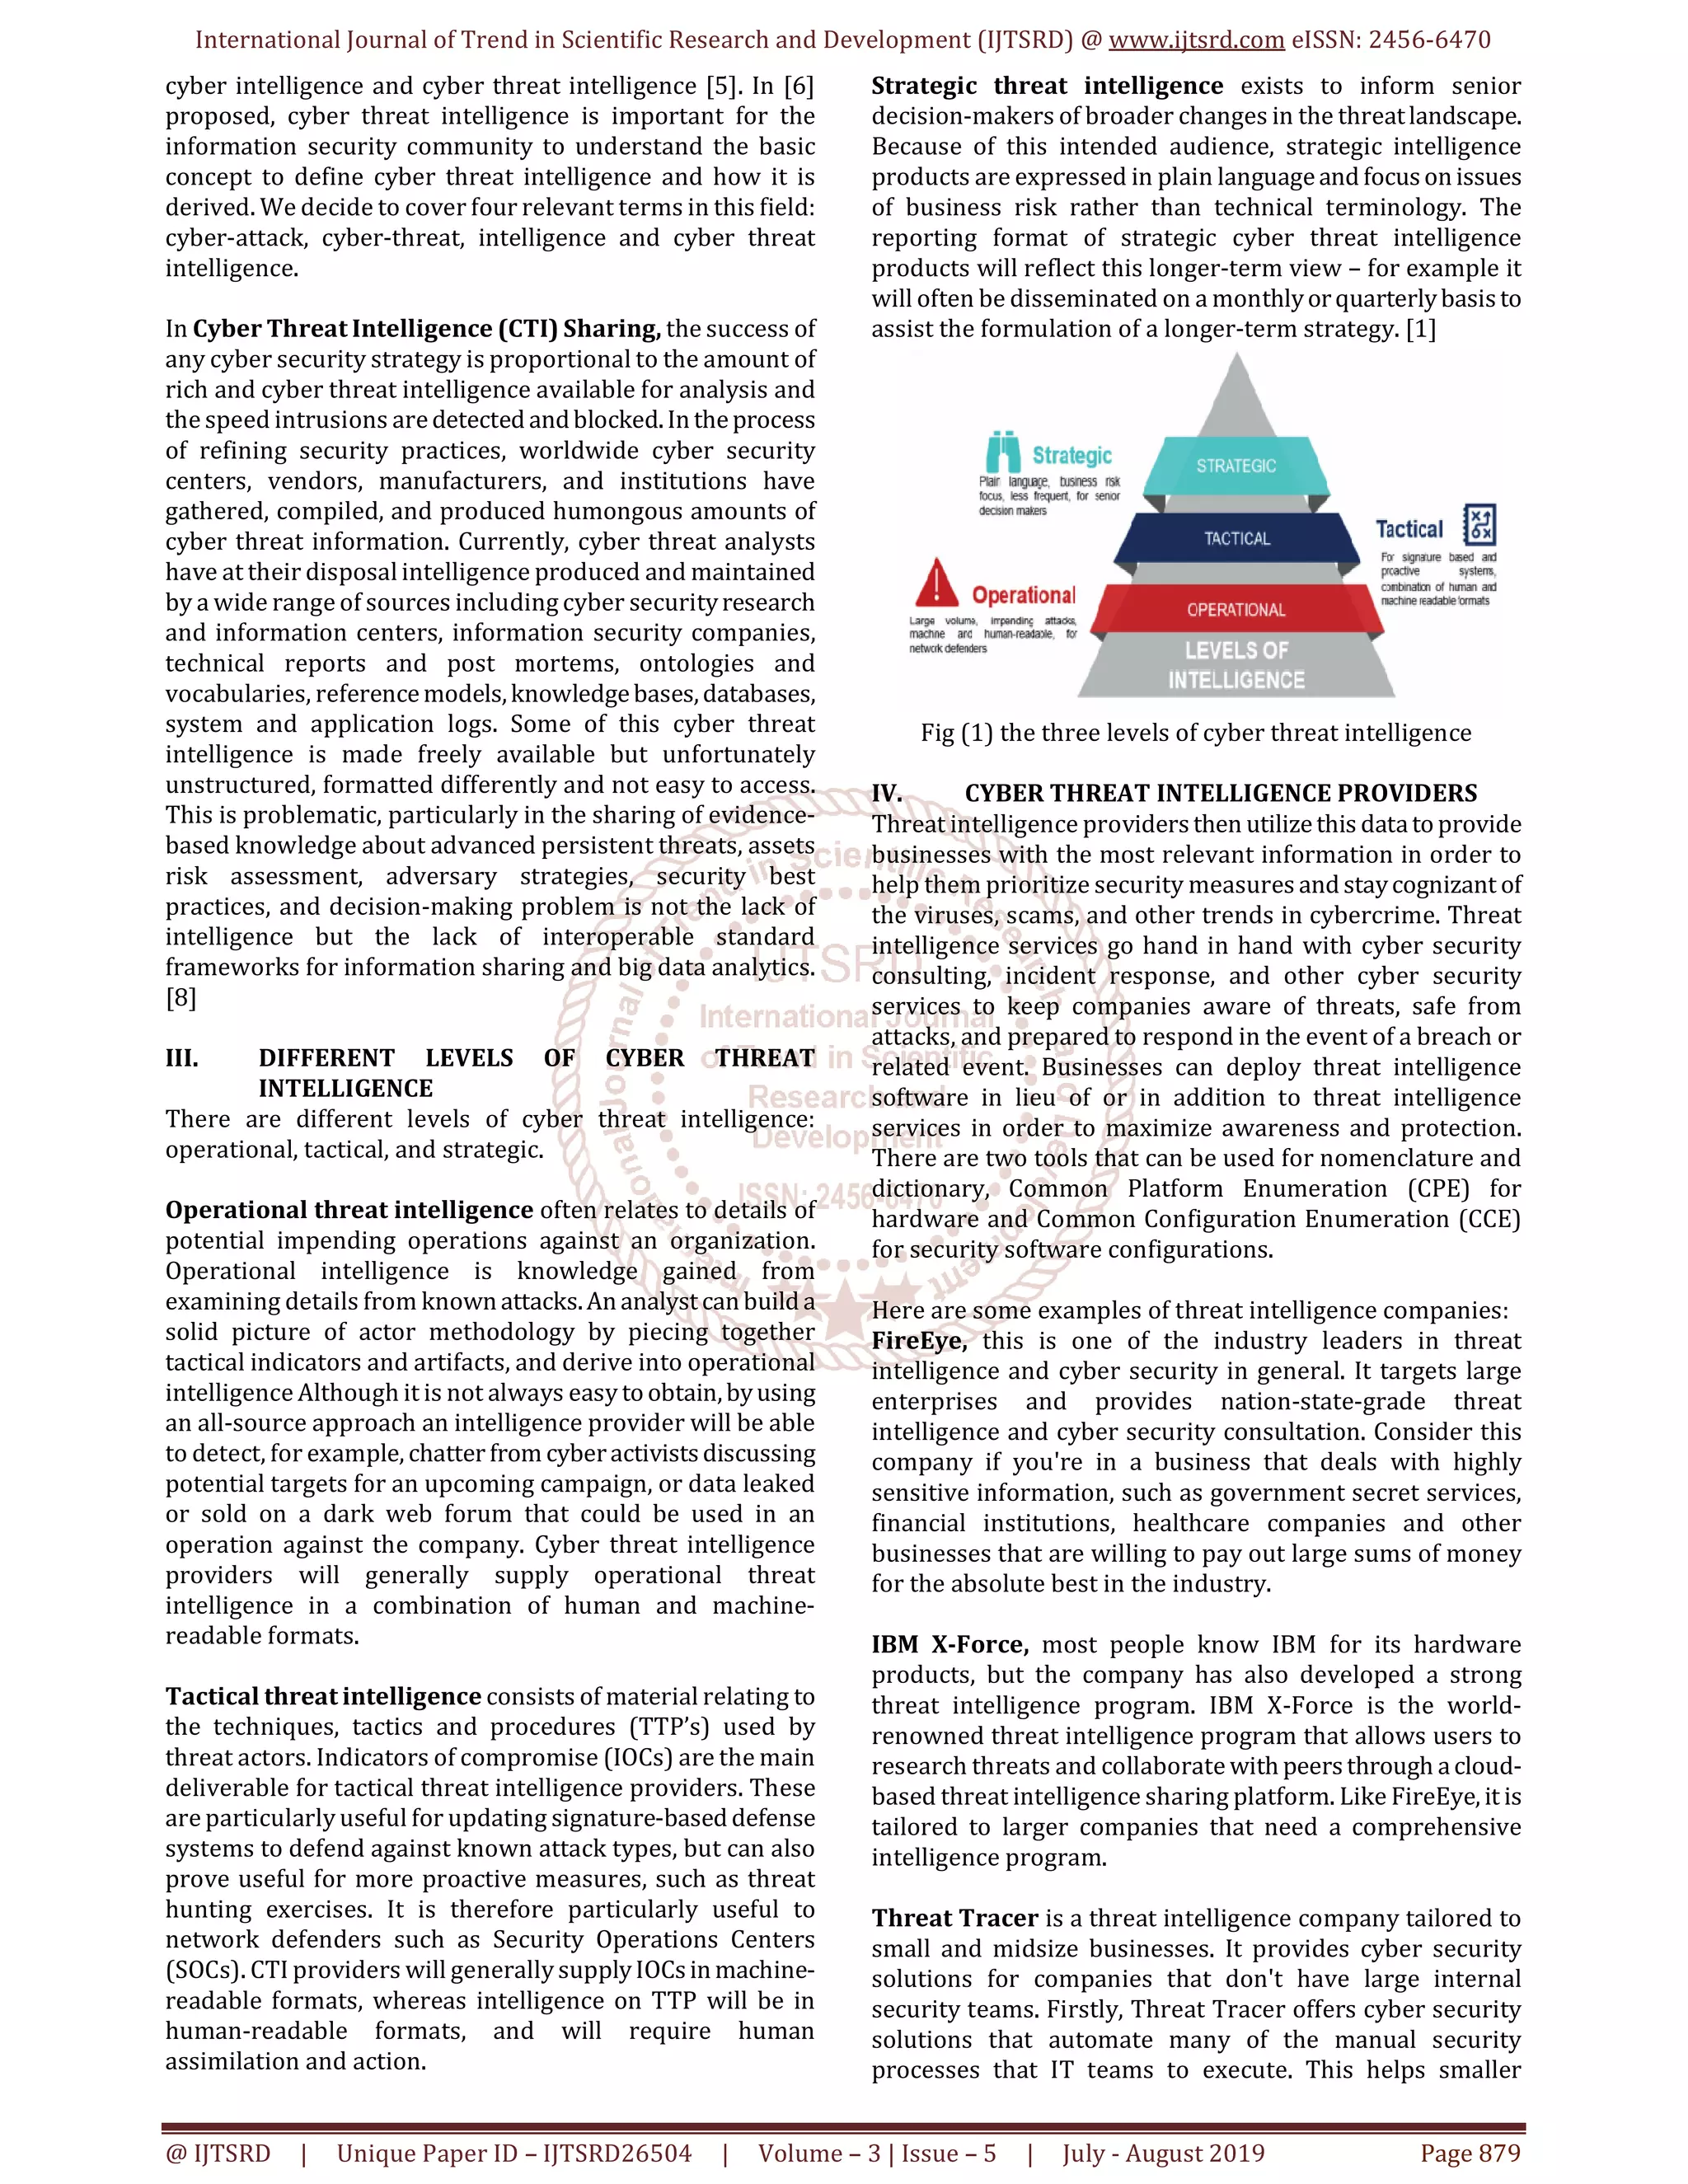
The methodology for assessing digital risk has undergone significant transformation. Historically, threat assessments relied on static indicators of compromise. Today, threat intelligence platforms integrate continuous telemetry, predictive artificial intelligence models, and real-time adversary behavior tracking.
Government agencies and private security sectors have converged on dynamic, multi-tiered grading systems. These frameworks move beyond simple color-coded alerts to incorporate contextual threat intelligence, distinguishing between opportunistic scanning, targeted espionage campaigns, and systemic supply chain infiltrations.
- Continuous Automated Scanning: Ingests millions of global telemetry events per second to flag anomalous behavior.
- Adversary Attribution Modeling: Evaluates the known techniques, tactics, and procedures of threat actors actively targeting specific sectors.
- Impact and Blast Radius Estimation: Calculates potential downtime, data exfiltration risk, and financial liability associated with an active campaign.
Comparative Analysis of Threat Escalation Tiers
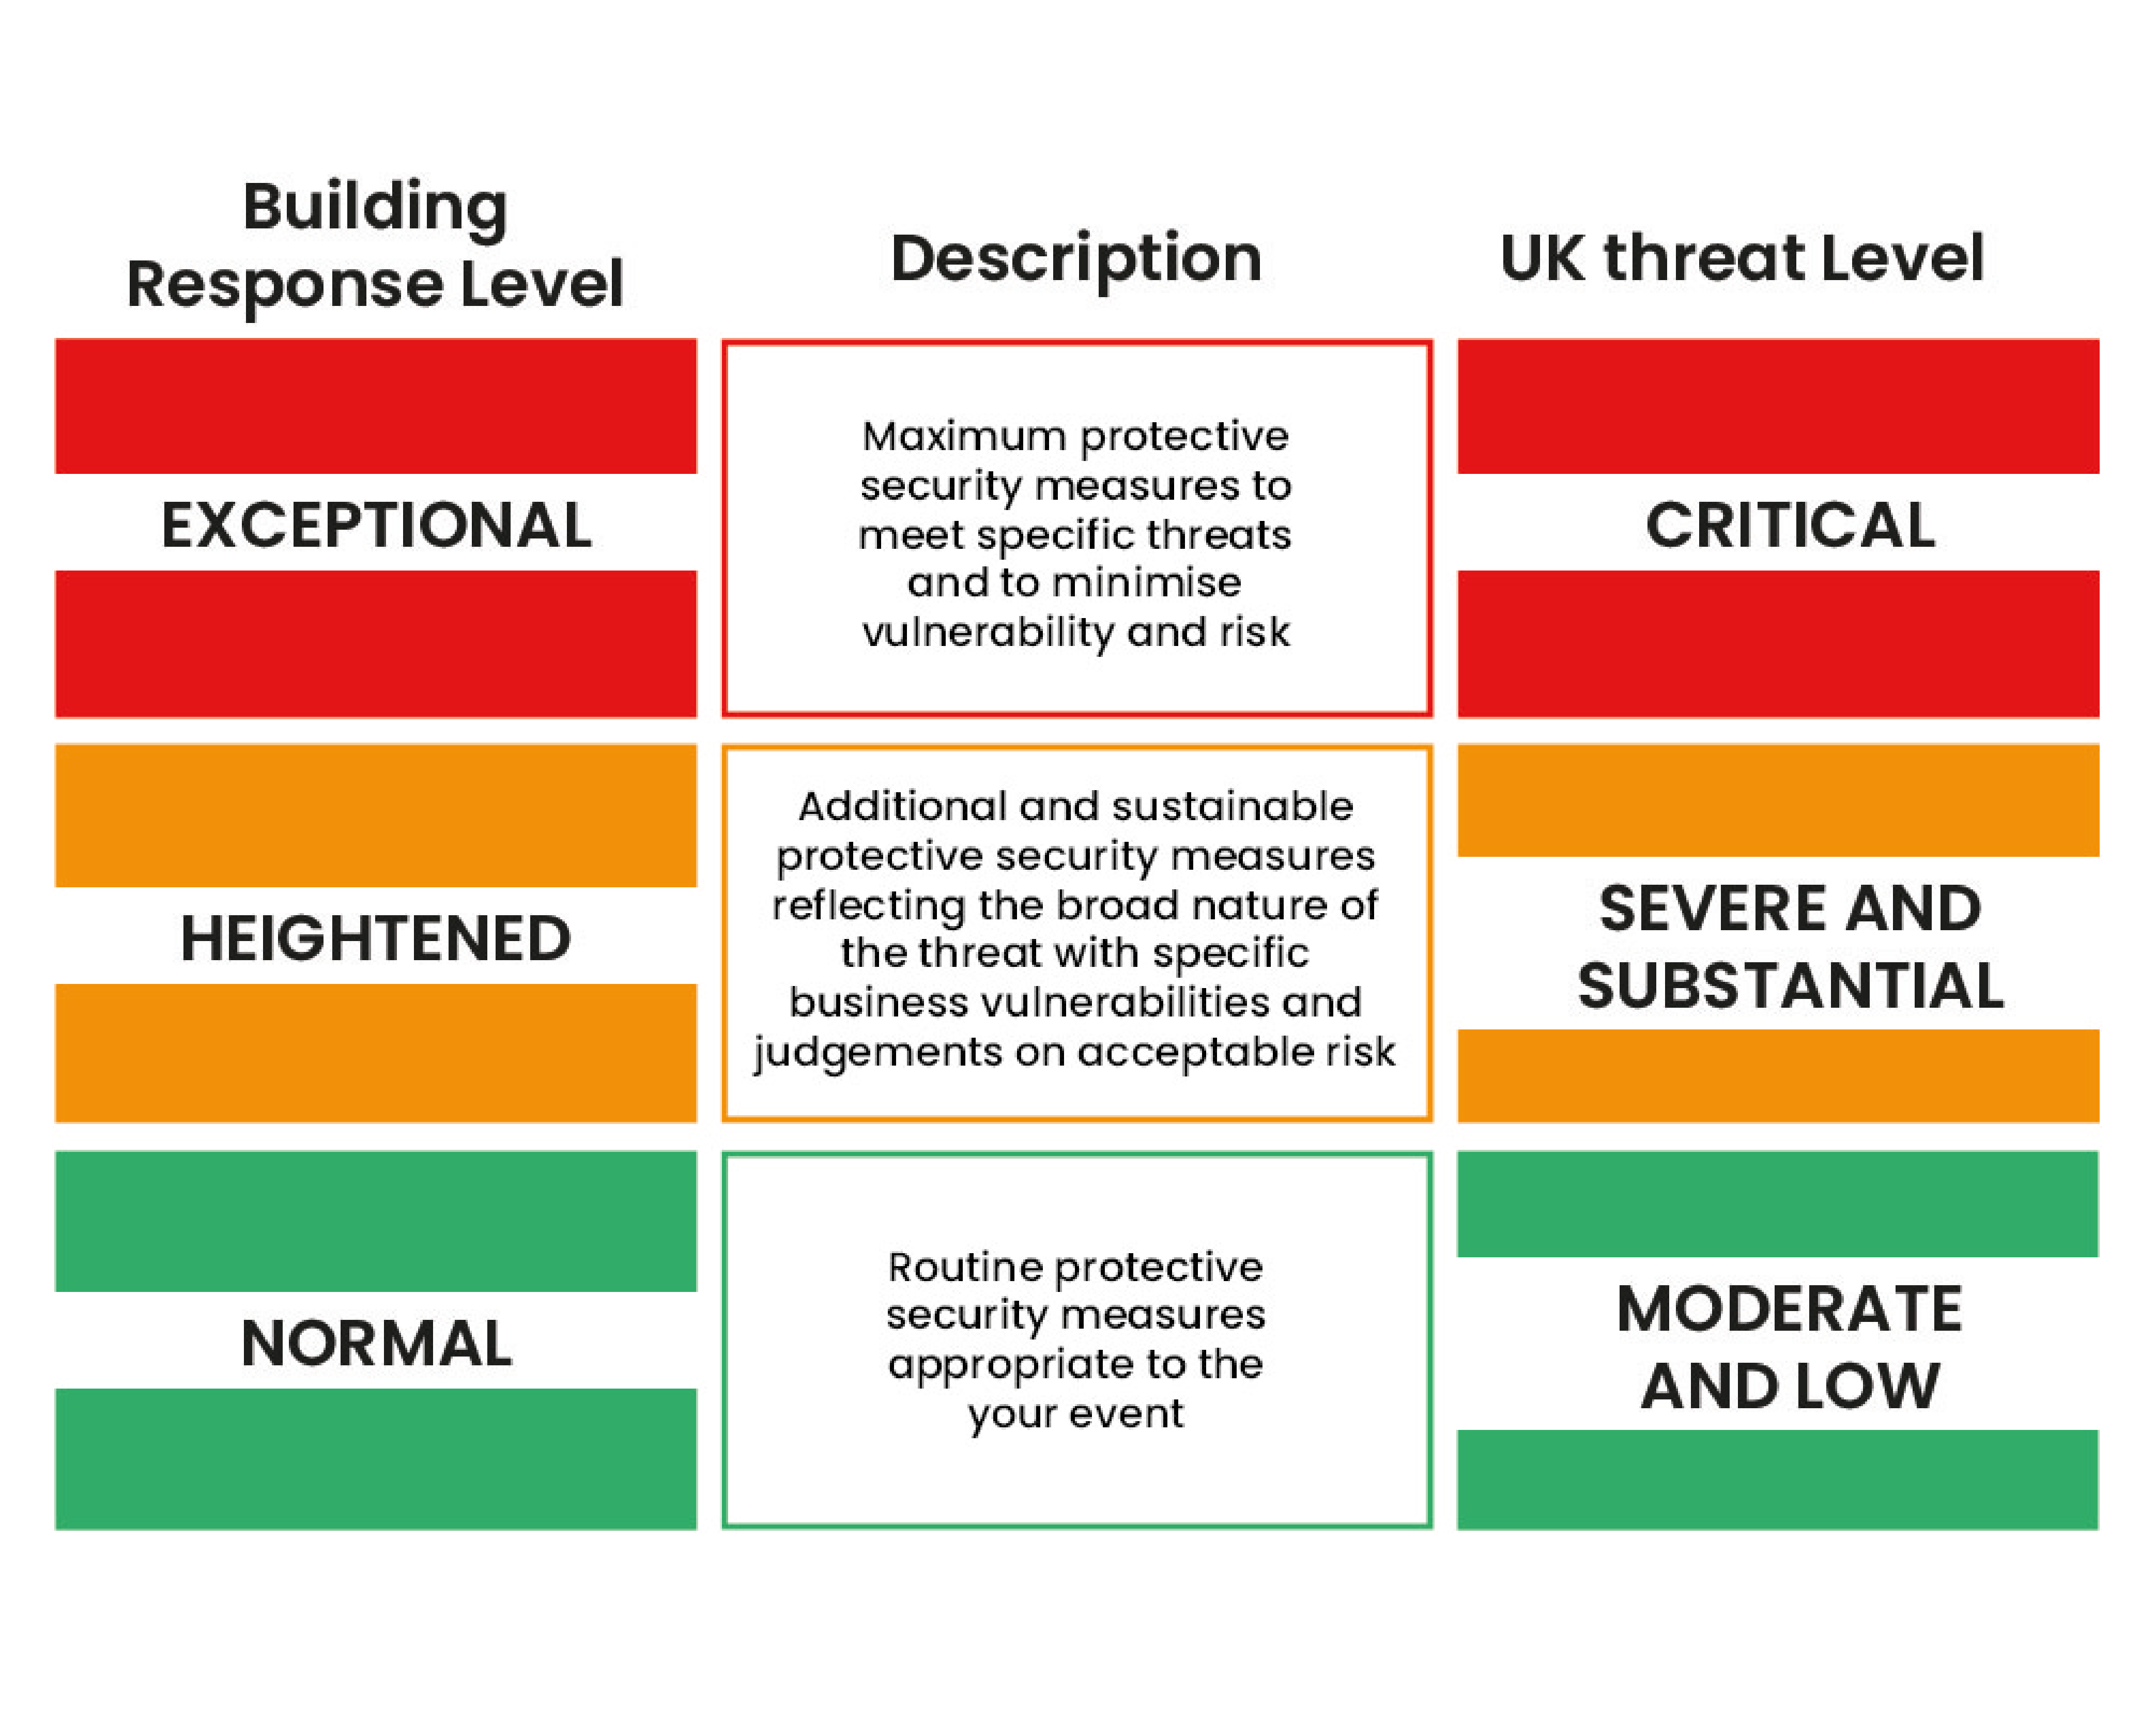
Understanding how different organizations translate threat intelligence into operational thresholds requires a clear comparative view. The table below outlines standard maturity levels, operational triggers, and required organizational responses within the 2026 threat landscape.
| Threat Tier | Operational Status | Key Triggers & Indicators | Mandatory Response Actions |
|---|---|---|---|
| Level 1 (Baseline) | Normal Operations | Standard background noise, routine phishing attempts, automated vulnerability scanning. | Standard monitoring, automated patching cycles, baseline endpoint protection. |
| Level 2 (Elevated) | Heightened Awareness | Verified exploit for a widely used software library with no patch currently available. | Accelerated patch testing, restriction of non-essential outbound ports, increased log retention. |
| Level 3 (High) | Active Threat Defense | Targeted phishing campaigns directed at executive staff or verified zero-day exploitation attempts against critical infrastructure. | Activation of incident response retainers, mandatory multi-factor authentication enforcement, isolation of high-value assets. |
| Level 4 (Critical) | Crisis Management | Active ransomware deployment, systemic network intrusion, or confirmed data exfiltration in progress. | Network segmentation execution, offline backup verification, engagement of legal and regulatory response teams. |
Core Components Driving Threat Level Calculations
Calculating an accurate cyber threat level involves synthesizing multiple distinct telemetry streams. Security operations centers rely on quantitative and qualitative metrics to eliminate guesswork during high-pressure scenarios.
Threat Intelligence Feeds and Indicator Quality
The accuracy of any threat level relies directly on the fidelity of ingested intelligence. High-grade intelligence filters out false positives, providing high-confidence indicators such as verified malicious command-and-control IP addresses, cryptographic hashes of novel malware variants, and domain names registered for typosquatting.
Asset Criticality and Network Topology
A vulnerability existing on an isolated development server carries a vastly different risk profile than the same vulnerability residing on a customer-facing payment gateway. Threat calculation engines weigh raw vulnerability data against asset classification databases, prioritizing systems based on data sensitivity, business continuity impact, and regulatory compliance obligations.
Strategic Implementation Guide for Security Teams
Operationalizing threat levels effectively prevents alert fatigue while ensuring rapid mobilization when legitimate danger arises. Security architects should follow a structured deployment model.
- Establish Clear Escalation Thresholds: Define explicit, quantitative criteria for shifting between threat levels. Avoid relying solely on subjective intuition.
- Automate Playbook Execution: Link threat level transitions directly to security orchestration, automation, and response platforms to instantly isolate compromised endpoints or revoke compromised credentials.
- Conduct Regular Tabletop Exercises: Simulate transitions to Level 3 and Level 4 threat states with cross-functional teams, including legal, public relations, and executive leadership, to ensure seamless communication during a crisis.
- Review and Refine Post-Incident: Following any elevation of the threat level, perform a comprehensive post-mortem to analyze detection latency, response efficacy, and framework adjustment needs.
Operational Mandate for Security Leaders
Threat levels must never remain static. If your organization operates at the exact same defensive posture year-round, your monitoring mechanisms are likely misaligned with the dynamic nature of modern cyber adversaries. Regular calibration ensures resources concentrate where risk is highest.
Pros and Cons of Standardized Threat Level Systems
Implementing a universal threat level framework offers distinct organizational advantages, but it also introduces notable operational challenges.
- Pros:
- Facilitates rapid communication between technical teams and non-technical executive leadership.
- Streamlines resource allocation during high-stress security incidents.
- Aligns internal defenses with broader national and industrial threat advisories.
- Cons:
- Risk of chronic alert fatigue if threshold triggers are set too sensitively.
- Potential for bureaucratic friction if rigid policies prevent agile responses to novel attacks.
- Complexity in accurately weighing multi-vector attacks against a single linear scale.
Frequently Asked Questions
What triggers an elevation in the national cyber threat level?
National threat levels typically elevate in response to credible, imminent intelligence regarding state-sponsored cyber espionage, widespread zero-day exploit campaigns against critical infrastructure, or geopolitical tensions that increase the likelihood of retaliatory digital warfare. This intelligence is evaluated by specialized government agencies and shared with private sector partners.
How do enterprise threat levels differ from public advisories?
Public advisories offer broad situational awareness for the general public or entire industries, whereas enterprise threat levels are custom-calibrated to an individual organization's specific network architecture, asset inventory, and unique risk profile. An enterprise might elevate its internal threat level due to a localized targeted attack even when national advisory levels remain stable.
Can automated tools completely manage threat level escalation?
Automated tools are essential for ingesting telemetry, detecting anomalies, and executing initial containment playbooks, but they cannot entirely replace human analytical judgment. Complex multi-stage intrusions require experienced security analysts to contextualize attacker intent and determine the appropriate strategic response tier.
What is the best way to prevent alert fatigue when using threat levels?
Preventing alert fatigue requires tuning detection rules based on asset criticality, reducing false positives through contextual enrichment, and ensuring that lower threat tiers trigger automated mitigation rather than manual paging of security staff. Human analysts should only be pulled into active response during genuine high-level escalations.
How often should an organization review its threat level criteria?
Organizations should conduct a formal review of their threat level escalation criteria at least annually, or immediately following any major infrastructure overhaul, significant merger or acquisition, or major shift in regulatory compliance frameworks.
Securing Your Digital Infrastructure Today
Maintaining resilience against sophisticated digital adversaries demands continuous vigilance, robust intelligence integration, and a clear operational framework. Evaluating your organization's threat level methodology allows you to transition from reactive scrambling to proactive, disciplined defense. Assess your current security posture, refine your escalation triggers, and ensure your teams are prepared to execute when threat levels rise.