The F95 API refers to the programmatic interface utilized by communities and platforms centered around adult gaming ecosystems, specifically interacting with databases like F95Zone. As of 2026, developers, data enthusiasts, and platform integrators require strict adherence to modern web standards, secure authentication protocols, and optimized rate-limiting strategies to build stable applications interacting with these services.
Understanding the F95 API Ecosystem and Core Infrastructure
Modern digital platforms rely on structured endpoints to deliver data efficiently. The architecture powering community gaming trackers and forum databases has shifted heavily toward token-based authentication, JSON-driven payloads, and asynchronous request handling. When building applications that consume data from community-driven sources, developers must prioritize payload minimization and respectful polling intervals to prevent server strain.
The primary communication channel involves HTTPS requests utilizing RESTful principles. Endpoints typically return structured JSON objects containing metadata about game releases, developer logs, version updates, and user-generated tags. Handling these payloads requires a robust backend capable of parsing nested arrays and managing relational data mappings securely.
Essential Data Entities Handled by the API
- Game Metadata: Titles, developer names, engine types (Ren'Py, Unity, Unreal Engine), and release timestamps.
- Version Control Strings: Current build numbers, patch notes, and update frequency metrics.
- Community Metrics: Rating scores, download counts, bookmark counts, and trending indicators.
- Categorization Tags: Genre classifications, content warnings, localization flags, and platform compatibility indicators.
Authentication Protocols and Security Best Practices
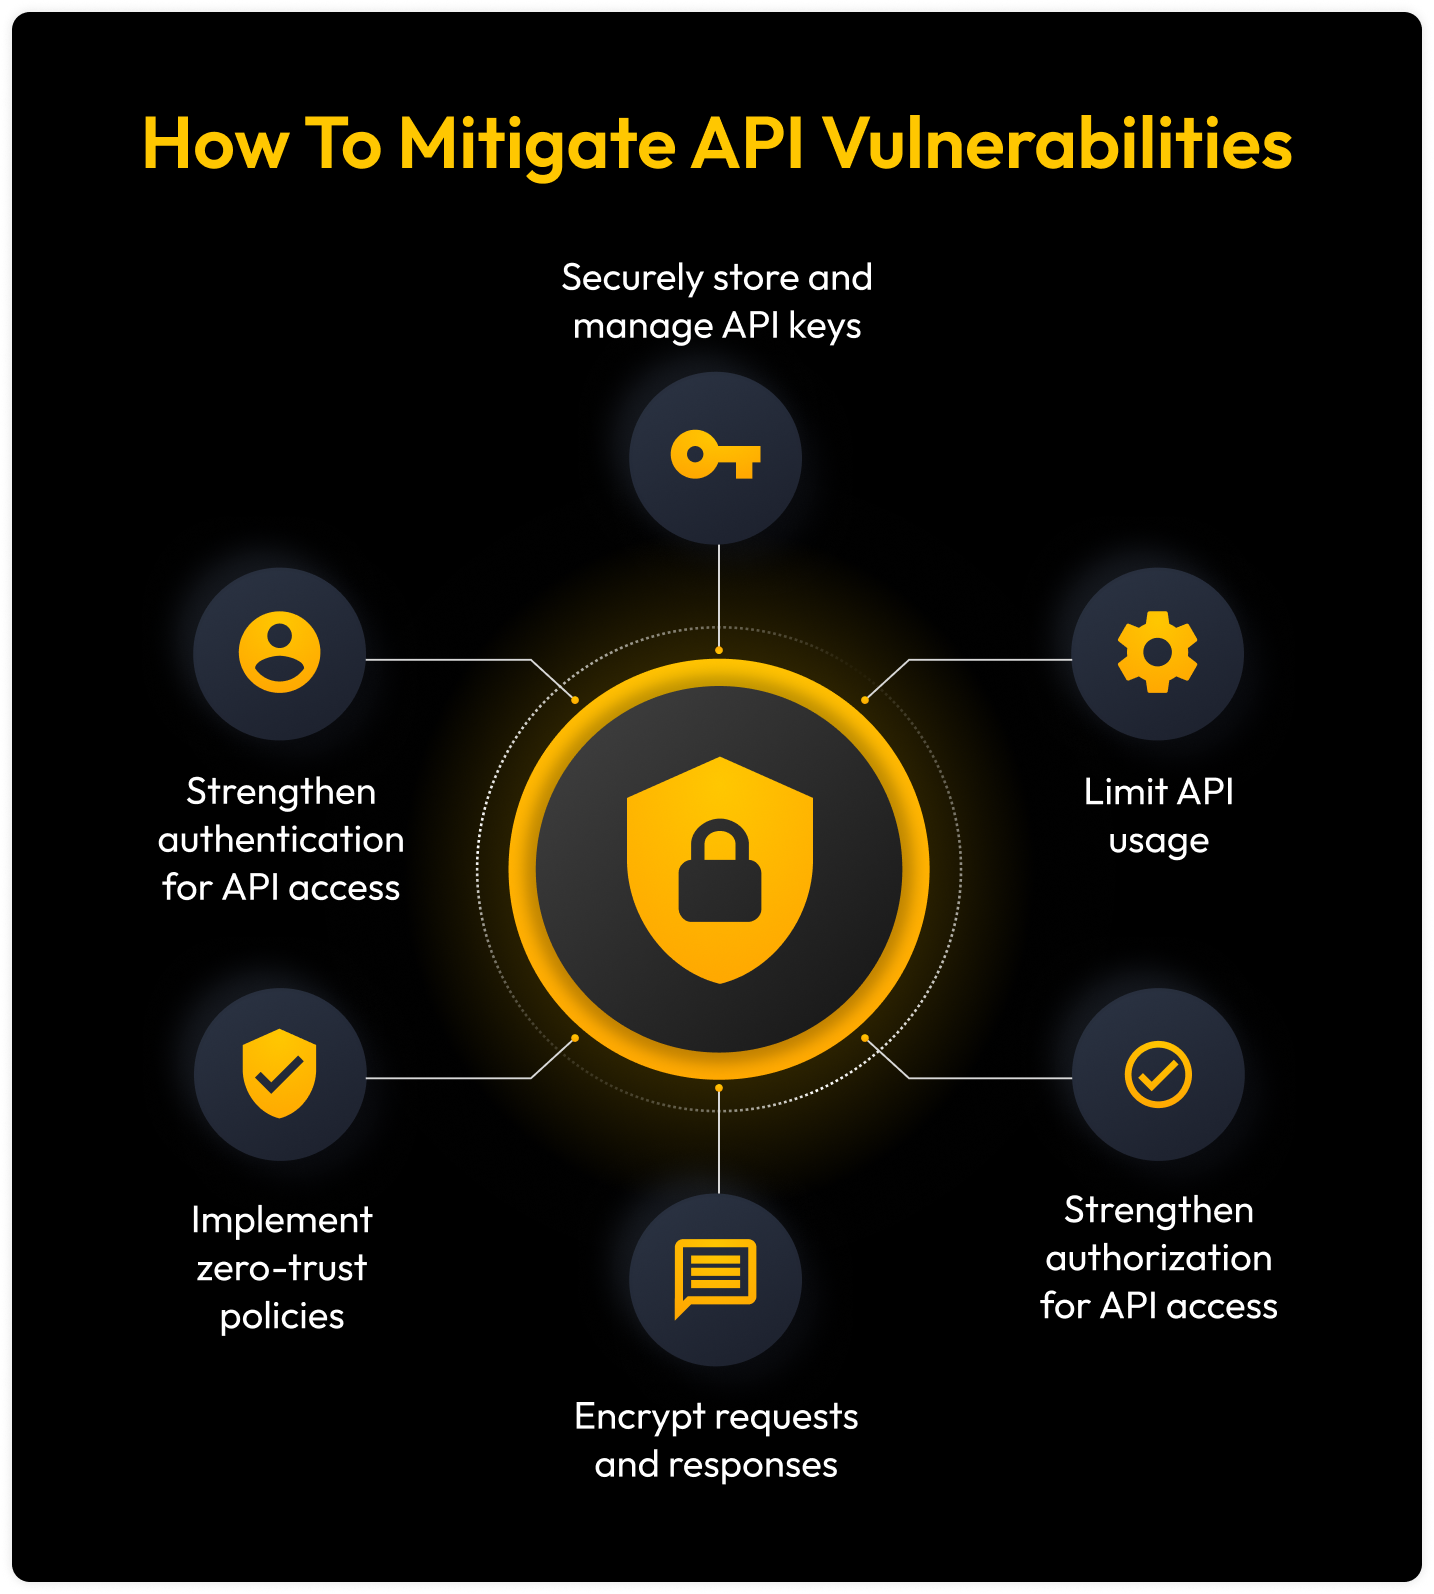
Securing communication between your client application and the API endpoints is paramount. In 2026, standard security measures dictate that plain-text token transmission is completely obsolete. Developers must implement OAuth 2.0 authorization flows or securely stored API keys injected via HTTP authorization headers.
Hardcoding credentials directly into client-side scripts exposes applications to unauthorized scraping and potential account suspension. Always route API requests through a secure backend proxy server. This masks sensitive keys from end-users and allows the implementation of caching layers, significantly reducing redundant external calls.
Security Mandate: Never expose administrative or high-privilege bearer tokens in public repositories or frontend JavaScript frameworks. Utilize environment variables and server-side secret management services to handle authentication handshakes.
Implementing Rate Limiting and Payload Optimization
Platform administrators strictly enforce rate limits to maintain server stability during peak traffic windows. Exceeding designated request thresholds typically results in temporary IP blacklisting or permanent API key revocation. Implementing exponential backoff algorithms in your error-handling logic ensures your application gracefully recovers from HTTP 429 Too Many Requests responses.
Payload optimization involves requesting only the fields required for your specific UI rendering. Instead of pulling entire database dumps, utilize query parameters to filter by date ranges, specific engines, or updated flags.
Comparison of Integration Strategies
| Strategy | Performance Impact | Security Risk | Maintenance Overhead |
|---|---|---|---|
| Direct Client-Side Polling | High (Client latency) | Critical (Exposed Keys) | Low |
| Backend Proxy with Caching | Optimal (Low latency) | Low (Secured Keys) | Medium |
| Webhook-Driven Sync | Near Zero (Event-based) | Low | High |
Step-by-Step Integration Workflow
Building a reliable integration requires a structured approach to connection establishment, error trapping, and data storage. Follow this chronological workflow to deploy a stable consumer application in 2026.
- Environment Provisioning: Set up a secure backend server (Node.js, Python FastAPI, or Go) equipped with modern HTTP client libraries like Axios or HTTPX.
- Authentication Handshake: Configure your environment variables to load authorization headers securely before initiating any outbound network traffic.
- Endpoint Mapping: Define the specific GET and POST routes your application requires, prioritizing read-only data synchronization to minimize risk exposure.
- Error Handling Implementation: Write robust try-catch blocks that capture HTTP status codes (401 Unauthorized, 403 Forbidden, 429 Too Many Requests, 500 Internal Server Error) and trigger fallback routines or alerts.
- Database Ingestion and Caching: Store retrieved JSON payloads in a localized database (PostgreSQL or MongoDB) to serve user requests without hammering the upstream provider.
Troubleshooting Common Connectivity Failures
Even well-architected applications encounter network interruptions and API response anomalies. Diagnosing these errors quickly minimizes downtime and preserves a smooth user experience.
- HTTP 401 Unauthorized: Usually indicates an expired or malformed bearer token. Verify that your environment variables are correctly synchronized and that token refresh logic is functioning.
- Timeout Errors: Large payloads or server-side throttling can cause connection timeouts. Implement a strict timeout threshold (e.g., 5 to 10 seconds) and retry requests using an exponential backoff schedule.
- Malformed JSON Responses: Upstream schema changes can break parsing scripts. Ensure your application includes schema validation libraries (such as Zod or Pydantic) to catch unexpected data structures before they crash your application state.
Frequently Asked Questions
What is the primary purpose of the F95 API?
The API allows authorized developers to programmatically retrieve metadata, game updates, and community statistics from forum-backed gaming databases. It enables the creation of third-party companion apps, launchers, and data aggregators.
How do I handle rate limiting effectively?
You should implement localized caching mechanisms to store frequently accessed data and use exponential backoff retry logic when encountering HTTP 429 status codes. Avoid aggressive polling loops.
Is client-side integration safe for production applications?
No. Direct client-side integration exposes sensitive API keys and authentication tokens to end-users, creating severe security vulnerabilities and increasing the risk of getting your IP banned.
What data formats are standard for API payloads?
JSON (JavaScript Object Notation) is universally used for request and response payloads due to its lightweight structure and native compatibility with modern programming languages.
How are breaking changes in the API managed?
Platform providers typically issue deprecation warnings and version their endpoints (e.g., v1 vs. v2). Developers must monitor official documentation channels to update their integration code before older versions are retired.
What should I do if my API requests are consistently timing out?
Check your network route, verify that you are not exceeding rate limits, and ensure the upstream servers are operational. Adding a caching layer on your backend will also reduce reliance on real-time external responses.
Conclusion and Next Steps
Integrating with community-driven platform APIs requires a disciplined approach to security, data caching, and error management. By routing requests through secure backend proxies, respecting rate limits, and designing resilient error-handling routines, developers can build stable, high-performance applications that scale effectively throughout 2026 and beyond.