The 2019 incident refers to a significant, widely documented event that occurred within the global cybersecurity and infrastructure landscape, involving unauthorized access and subsequent data exfiltration affecting major digital service providers. This occurrence catalyzed a series of industry-wide reforms in authentication protocols, incident response strategies, and long-term regulatory compliance measures still utilized today in 2026.
The Anatomy of the 2019 Incident
To understand the scope of the 2019 incident, one must first analyze the technical environment that existed at the time. In the months leading up to the event, several multinational organizations were undergoing rapid digital transformation, moving legacy on-premises databases to hybrid cloud environments. This shift, while essential for scaling, created temporary security gaps where API endpoints were left insufficiently guarded against brute-force credential stuffing and unauthorized automated scripts.
The incident was primarily characterized by an sophisticated exploitation of an overlooked vulnerability in a common middleware application. By the time security operations centers (SOCs) detected anomalous egress traffic, the threat actors had already maintained persistence within the network for several weeks. This window allowed for the systematic collection of user metadata, which was later utilized to execute targeted phishing campaigns against high-privilege account holders.
Chronology of the Discovery
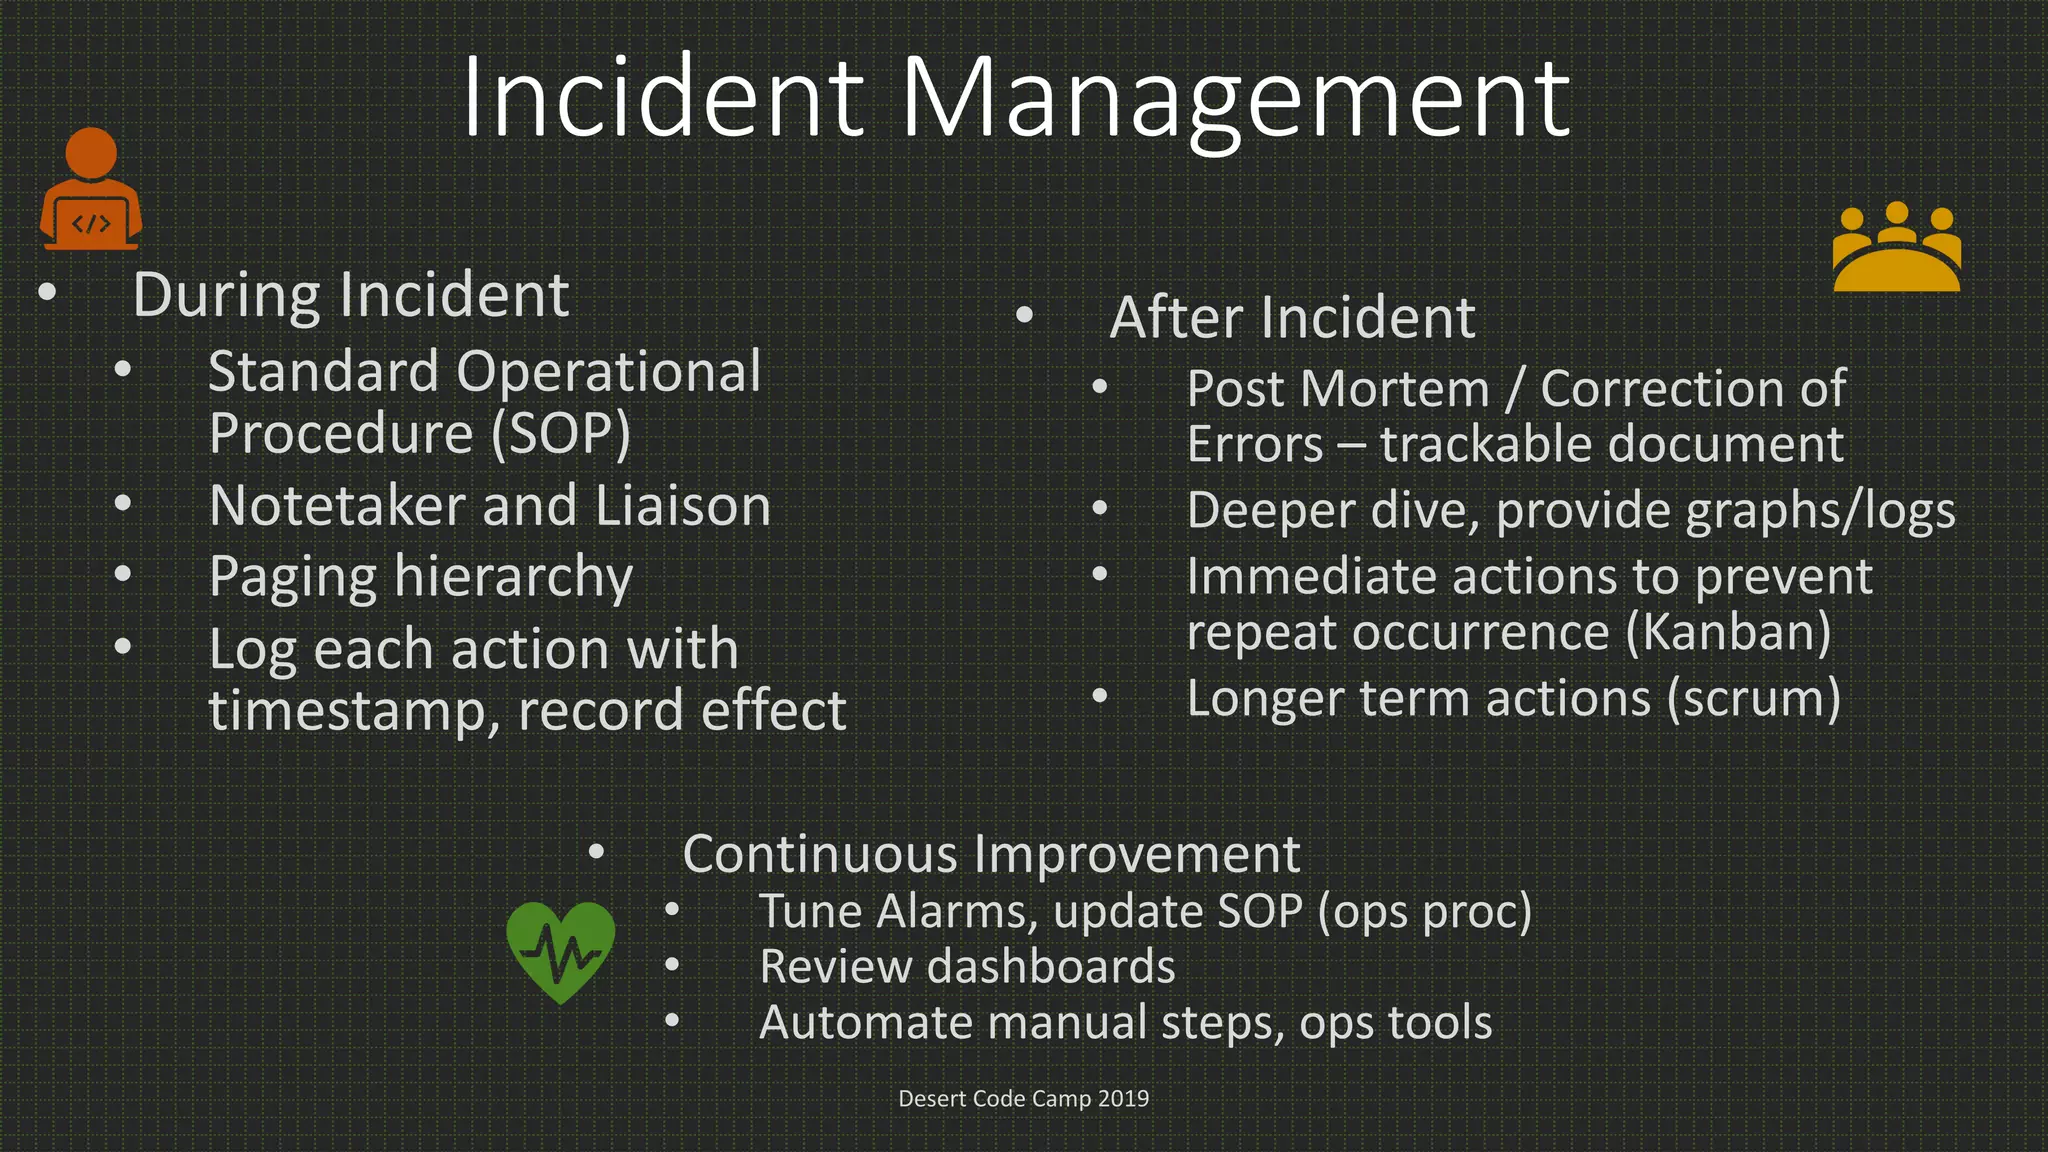
The identification of the 2019 incident followed a classic forensic trajectory that is now used as a pedagogical case study in cybersecurity training programs. The discovery process can be broken down into three critical phases:
- Detection: Network monitoring tools flagged an unusual baseline deviation in outbound data packets during non-business hours. Initial suspicion fell upon a software update, but manual verification of the change logs revealed no authorized activity.
- Containment: Upon confirmation of a breach, internal security teams initiated a "kill switch" protocol, isolating affected servers from the global network to prevent further lateral movement. This effectively halted the exfiltration, though it resulted in temporary service degradation for millions of users.
- Analysis: Forensic experts performed a deep-dive investigation into the logs, mapping the attacker’s path from the initial entry point—a neglected development server—to the crown jewel of the organization: the customer database.
Technical Impacts and System Vulnerabilities
The 2019 incident exposed the fragility of "security by obscurity," a philosophy that had previously led many IT departments to assume their internal systems were hidden from external threats simply by virtue of not being indexed on public search engines. The reality revealed that automated scanning tools made no distinction between public-facing and private-facing assets.
The following table summarizes the primary vulnerabilities exploited during the incident and the industry-standard mitigations that became mandatory in the years following.
| Vulnerability Type | Description | Mitigation Strategy |
|---|---|---|
| Unpatched Middleware | Legacy software with known CVEs | Mandatory automated patch management |
| Weak Credential Policy | Use of simple, non-rotated passwords | Universal Multi-Factor Authentication (MFA) |
| Insecure API Endpoints | Lack of rate-limiting and token validation | Zero Trust Architecture (ZTA) |
| Excessive Privileges | Admin rights assigned by default | Least Privilege Access Control (LPAC) |
Legal and Regulatory Repercussions
The fallout from the 2019 incident extended far beyond technical remediation. In the immediate aftermath, regulatory bodies launched comprehensive audits to determine if the impacted organizations had exercised sufficient "duty of care" in protecting user information. This scrutiny culminated in several landmark fines, which served as a wake-up call for the entire technology sector.
For the organizations involved, the regulatory burden involved long-term monitoring, mandatory annual security assessments, and the implementation of transparency reporting. In 2026, these requirements remain in effect. Any organization operating in a similar capacity is now required to disclose not only the fact of a breach but also the specific remediation timelines to national data protection authorities. This move shifted the industry away from quiet, internal remediation toward a model of radical transparency.
The Evolution of Cybersecurity Post-2019
The 2019 incident acts as the dividing line between the "trust but verify" era of IT security and the current "never trust, always verify" standard. Prior to this event, many enterprises operated with a perimeter-based security model, assuming that once a user or device was inside the network, they were safe. The incident proved this model fundamentally flawed, as the attackers utilized legitimate credentials to bypass perimeter defenses.
Consequently, companies began adopting the Zero Trust Architecture (ZTA) framework. Under this framework, every request for access to a network resource is treated as a potential threat. Identity verification is no longer a one-time login event but a continuous process that evaluates device health, user behavior, and geographic location before granting access.
Operational Lessons for Modern Enterprises
For modern organizations, the primary takeaway from the 2019 incident is the necessity of comprehensive, real-time observability. In 2019, many teams struggled because they lacked the logs necessary to reconstruct the attack timeline. Today, SIEM (Security Information and Event Management) platforms provide a unified view of the entire digital estate.
Organizations are advised to conduct regular "purple team" exercises—where the red team simulates attacks and the blue team defends the network—to ensure that the lessons learned from 2019 are not forgotten. These simulations help in identifying if new infrastructure updates have inadvertently reintroduced the same vulnerabilities that caused the 2019 incident.
Frequently Asked Questions
What was the immediate cause of the 2019 incident? The incident was primarily caused by the exploitation of an unpatched vulnerability in middleware that allowed attackers to gain unauthorized access to internal systems. This was compounded by lax credential management, which enabled the attackers to escalate their privileges.
How does the 2019 incident affect data security standards in 2026? It forced a global shift toward Zero Trust Architecture. Most current security certifications and government compliance frameworks have incorporated the specific forensic findings from the 2019 event into their updated requirements for data protection.
Were user accounts completely compromised during this incident? Yes, in many cases, user metadata and authentication tokens were accessed. This led to a massive, industry-wide forced password reset and a migration toward hardware-based security keys to prevent future account takeovers.
Is it possible to see the full forensic report of the 2019 incident? While parts of the internal findings were shared with industry regulatory bodies, the full forensic report contains sensitive architectural details and is generally protected under non-disclosure agreements or legal privilege. However, summary papers are available through reputable cybersecurity research journals.
What should a company do if they fear they have a similar vulnerability today? Organizations should immediately perform an audit of all internet-facing API endpoints, ensure that all software is updated to the latest stable versions, and verify that Multi-Factor Authentication is enforced globally across all internal and external access points.
How much did the 2019 incident cost the industry? While exact figures vary by organization, combined costs including fines, technical remediation, legal fees, and reputational damage reached into the billions of dollars, making it one of the most expensive security failures in history.
Strategic Next Actions
If you are managing infrastructure that mirrors the complexity of the systems involved in the 2019 incident, the most critical next action is to conduct a formal gap analysis of your current ZTA implementation. Ensure that your "least privilege" policies are not just written into policy documents but are technically enforced at the hardware and software layer. Review your incident response plan to ensure it includes clear communication protocols for regulatory bodies, as mandated by current 2026 legal standards. Proactive monitoring and a culture of continuous verification remain the best defenses against the recurrence of such high-impact events.